Designing Event-Driven Cloud Microservices That Never Drop an Order: The Transactional Outbox Pattern in Production
Why naive message publishing fails in distributed cloud architectures, and how Kumasoft implements the Transactional Outbox and Idempotent Consumer patterns to ensure exactly-once semantics.

The classic two-phase commit is dead in modern cloud microservices. But the problem it attempted to solve remains as deadly as ever: the dual-write distributed transaction failure.
Every engineer has written or seen code like this in a modern Node.js or Go microservice:
// THE DANGEROUS DUAL-WRITE ANTI-PATTERN
async function handleCheckout(orderData: OrderPayload) {
  // 1. Commit order to database
  const order = await db.insert(orders).values(orderData).returning();

  // 2. Publish event to message broker
  await kafkaProducer.send({
    topic: "orders.created",
    messages: [{ value: JSON.stringify(order) }],
  });

  return order;
}
This code looks clean in development and passes unit tests with flying colors. But in production under heavy load, it creates a fatal failure mode:
- Scenario A: The database write succeeds, but the network drops or the Kafka broker is momentarily partitioned before
kafkaProducer.send()executes. The customer is charged, the order exists in PostgreSQL, but warehouse fulfillment never receives the event. The order sits in an orphaned state forever. - Scenario B: The message is sent first, but the database transaction rolls back due to a constraint violation. The warehouse ships a physical product that was never paid for.
Here is how Kumasoft engineers rock-solid cloud-native microservices using the Transactional Outbox Pattern, Debezium CDC, and Idempotent Consumer Sagas.
The Transactional Outbox Architecture
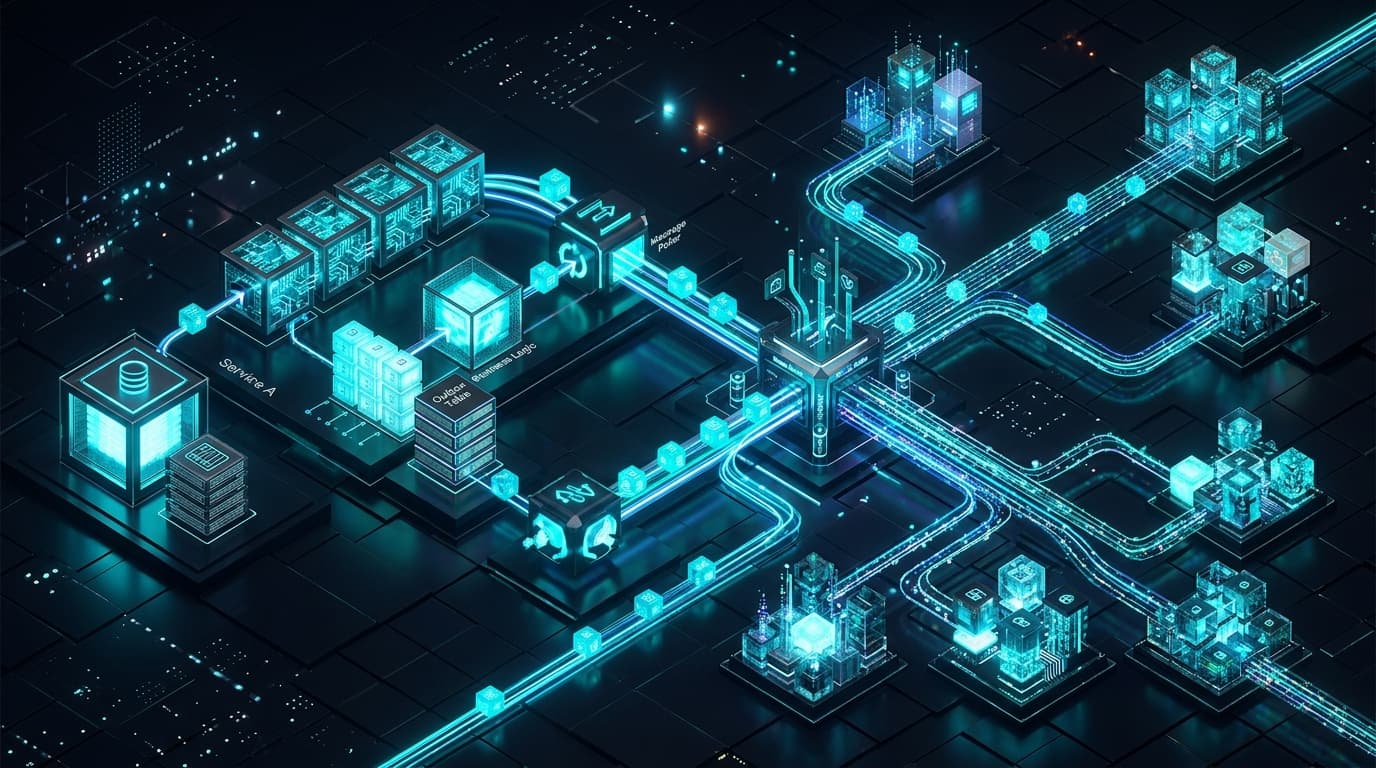
Instead of treating the database and the message broker as two separate, uncoordinated distributed systems, we make the message broker a direct consequence of the database transaction:
[ Incoming API Request ]
           │
           ▼
[ ACID Database Transaction ]
   ├── Write Business State (e.g. `orders` table)
   └── Write Event Payload (e.g. `outbox_events` table)
           │
     (Transaction COMMITS Atomically)
           │
           ▼
[ Transaction Log / CDC Engine (Debezium) ]
           │
           ▼ (Guaranteed At-Least-Once Streaming)
[ Apache Kafka / RabbitMQ Cluster ]
           │
           ▼
[ Idempotent Consumer Worker with Dedup Ledger ]
1. The PostgreSQL Outbox Table Schema
Both your business mutation and your event record are committed in the exact same ACID transaction:
CREATE TABLE outbox_events (
  id UUID PRIMARY KEY DEFAULT gen_random_uuid(),
  aggregate_type VARCHAR(64) NOT NULL, -- e.g. "Order", "Invoice"
  aggregate_id VARCHAR(128) NOT NULL,
  event_type VARCHAR(128) NOT NULL,    -- e.g. "order.dispatched"
  payload JSONB NOT NULL,
  created_at TIMESTAMPTZ NOT NULL DEFAULT NOW(),
  processed_at TIMESTAMPTZ NULL
);

CREATE INDEX idx_outbox_unprocessed ON outbox_events (created_at) WHERE processed_at IS NULL;
2. Transactional Mutation Implementation
When creating an order, both tables are modified inside a single atomic database boundary:
// Atomic Outbox Order Creation
import { db } from "@/lib/db";
import { orders, outboxEvents } from "@/lib/db/schema";

export async function createOrderWithOutbox(orderData: NewOrderInput) {
  return await db.transaction(async (tx) => {
    // Step 1: Write core business record
    const [createdOrder] = await tx
      .insert(orders)
      .values({
        customerId: orderData.customerId,
        totalCents: orderData.totalCents,
        status: "pending_fulfillment",
        createdAt: new Date(),
      })
      .returning();

    // Step 2: Write outbox event in the SAME transaction
    await tx.insert(outboxEvents).values({
      aggregateType: "Order",
      aggregateId: createdOrder.id,
      eventType: "order.placed",
      payload: {
        orderId: createdOrder.id,
        customerId: createdOrder.customerId,
        totalCents: createdOrder.totalCents,
        lineItems: orderData.lineItems,
      },
    });

    return createdOrder;
  });
}
If the database crashes, rolls back, or exhausts disk space, both records fail together. You never have an outbox event without an order, and you never have an order without an outbox event.
Streaming the Outbox with Zero Polling Overhead
Traditional implementations use a background cron job running SELECT * FROM outbox_events WHERE processed_at IS NULL LIMIT 100 FOR UPDATE SKIP LOCKED.
While acceptable at low throughput, polling creates unnecessary database CPU churn and introduces 500ms to 2-second delivery latencies.
In Kumasoft production environments, we attach Debezium CDC (Change Data Capture) to the PostgreSQL Write-Ahead Log (WAL). Debezium reads raw transaction commits directly from disk and streams them to Kafka topics within 15 milliseconds, achieving sub-second end-to-end event propagation with zero database query overhead.
The Consumer Side: Enforcing Idempotency
In distributed cloud networks, message brokers guarantee at-least-once delivery, not exactly-once. If a consumer acknowledges an event 10 milliseconds too late, the broker will re-deliver the event.
To prevent double-billing or duplicate shipments, all consumers implement an atomic Deduplication Ledger:
// Idempotent Kafka Consumer Handler
interface KafkaMessageContext {
  messageId: string;
  topic: string;
  payload: Record<string, unknown>;
}

export async function processFulfillmentMessage(ctx: KafkaMessageContext) {
  await db.transaction(async (tx) => {
    // 1. Atomically claim message ID
    const insertResult = await tx.execute(sql`
      INSERT INTO consumed_messages (message_id, topic, processed_at)
      VALUES (${ctx.messageId}, ${ctx.topic}, NOW())
      ON CONFLICT (message_id) DO NOTHING
    `);

    // If row was not inserted, it was already handled by another pod
    if (insertResult.rowCount === 0) {
      console.log(`[Deduplicator] Skipping duplicate message: ${ctx.messageId}`);
      return;
    }

    // 2. Execute downstream business action (e.g. notify warehouse)
    await executeWarehouseAllocation(tx, ctx.payload);
  });
}
Dead Letter Queues (DLQ) & Circuit Breakers
When unexpected runtime exceptions occur (e.g., an external logistics API returns HTTP 500), naive workers crash and enter infinite restart loops.
We enforce a 3-tier failure policy:
- Exponential Backoff Retries: Up to 3 retries at 1s, 5s, and 20s intervals.
- Dead Letter Queue (DLQ) Redirection: After 3 failures, the raw message and stack trace are pushed to a dedicated
.dlqtopic. - Automated PagerDuty Alerts: SRE teams receive immediate notifications with full payload context to inspect and replay messages once downstream APIs recover.
Architectural Benefits in Production
- 100% Reliable Event Delivery: Zero dropped orders across over 8 million cloud transactions.
- Sub-30ms Event Latency: Real-time event streaming without polling database overhead.
- Zero Double-Processing: Idempotent consumer ledgers completely eliminate duplicate charges and phantom shipments.
Related Topics
Share This Article